
Some of the common log4j appenders. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of. Dec 10, 2021 · apache log4j 2 is widely used in many popular software applications, such as apache struts, elasticsearch, redis, kafka and others. 7.4.0 to 7.7.3, 8.0.0 to 8.11.0. 6), the vulnerable configurations have been disabled by default.
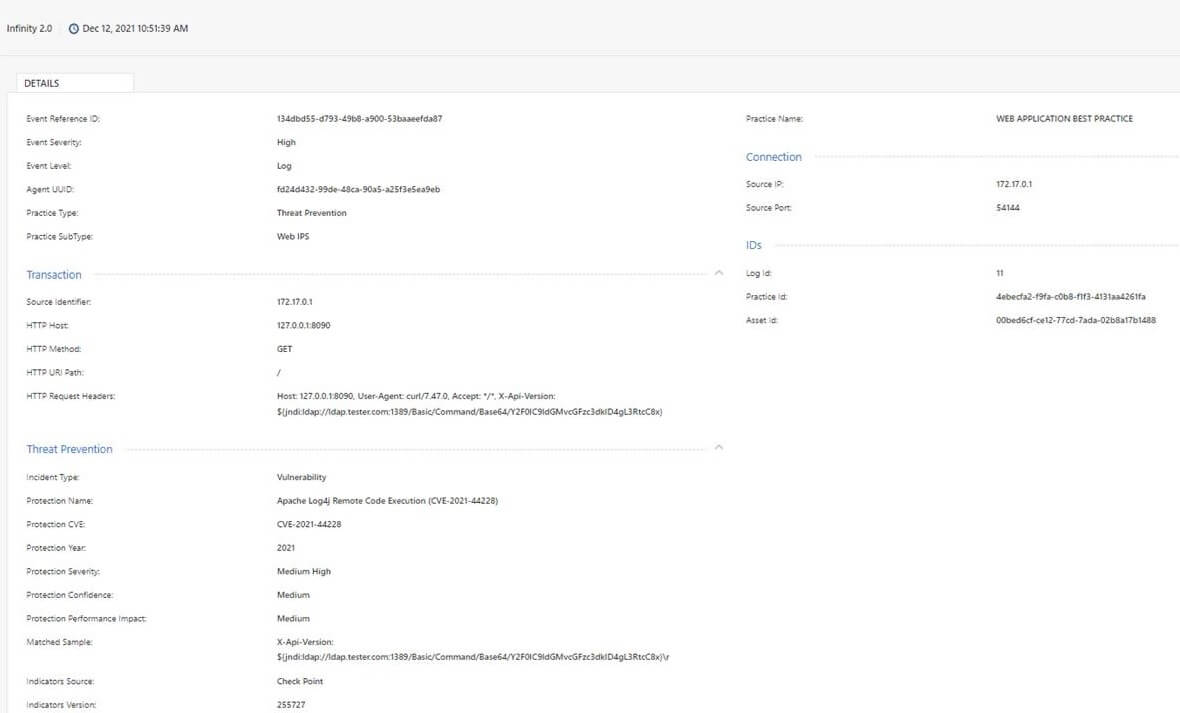
Dec 13, 2021 · apache released log4j version 2.15.0 in a security update to address this vulnerability.
Apache log4j is also part of a project which is known as apache logging. It is part of the apache logging services, a project of the apache software foundation.log4j is one of several java logging frameworks. Welcome to apache log4j, a logging library for java. For full impact and additional detail consult the log4j security page. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of the improvements available in logback while fixing some inherent problems in logback's architecture. However, in order for the vulnerability to be remediated in products and services that use affected versions of log4j, the maintainers of those products and services must implement this security update. For more info, please see the apache software foundation. Dec 13, 2021 · apache log4j 2. Dec 13, 2021 · apache released log4j version 2.15.0 in a security update to address this vulnerability. The apache log4j team developed log4j 2 in response to the. Some of the common log4j appenders. As of log4j 2.0.15 (released on dec. While supplying an easy and flexible user experience, apache log4j 2 has historically been vulnerable to process and deserialize user inputs.
While supplying an easy and flexible user experience, apache log4j 2 has historically been vulnerable to process and deserialize user inputs. Apache log4j is an apache software foundation project and developed by a dedicated team of committers of the apache software foundation. Apache solr releases prior to 8.11.1 were using a bundled version of the apache log4j library vulnerable to rce. Dec 13, 2021 · apache released log4j version 2.15.0 in a security update to address this vulnerability. As of log4j 2.0.15 (released on dec.
Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of.
While supplying an easy and flexible user experience, apache log4j 2 has historically been vulnerable to process and deserialize user inputs. However, in order for the vulnerability to be remediated in products and services that use affected versions of log4j, the maintainers of those products and services must implement this security update. Apache solr releases prior to 8.11.1 were using a bundled version of the apache log4j library vulnerable to rce. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of. Dec 13, 2021 · apache log4j 2. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of the improvements available in logback while fixing some inherent problems in logback's architecture. Welcome to apache log4j, a logging library for java. The version of 1.x have other vulnerabilities, we recommend that you … As of log4j 2.0.15 (released on dec. For more info, please see the apache software foundation. 6), the vulnerable configurations have been disabled by default. For full impact and additional detail consult the log4j security page. May 13, 2012 · apache log4j™ 1.2.
Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of. For full impact and additional detail consult the log4j security page. Gülcü has since started the slf4j and logback projects, with the intention of offering a successor to log4j. For more info, please see the apache software foundation. 7.4.0 to 7.7.3, 8.0.0 to 8.11.0.

It is part of the apache logging services, a project of the apache software foundation.log4j is one of several java logging frameworks.
It is part of the apache logging services, a project of the apache software foundation.log4j is one of several java logging frameworks. 6), the vulnerable configurations have been disabled by default. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of the improvements available in logback while fixing some inherent problems in logback's architecture. For full impact and additional detail consult the log4j security page. Gülcü has since started the slf4j and logback projects, with the intention of offering a successor to log4j. However, in order for the vulnerability to be remediated in products and services that use affected versions of log4j, the maintainers of those products and services must implement this security update. Dec 13, 2021 · apache released log4j version 2.15.0 in a security update to address this vulnerability. Some of the common log4j appenders. Apache solr releases prior to 8.11.1 were using a bundled version of the apache log4j library vulnerable to rce. Dec 13, 2021 · apache log4j 2. Apache log4j is an apache software foundation project and developed by a dedicated team of committers of the apache software foundation. Apache log4j is also part of a project which is known as apache logging. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of the improvements available in logback while fixing some inherent problems in logback's architecture.
Apache Log4J : 5yslem1jwxv1am - However, in order for the vulnerability to be remediated in products and services that use affected versions of log4j, the maintainers of those products and services must implement this security update.. May 13, 2012 · apache log4j™ 1.2. Apache log4j 2 is an upgrade to log4j that provides significant improvements over its predecessor, log4j 1.x, and provides many of the improvements available in logback while fixing some inherent problems in logback's architecture. 6), the vulnerable configurations have been disabled by default. However, in order for the vulnerability to be remediated in products and services that use affected versions of log4j, the maintainers of those products and services must implement this security update. Dec 13, 2021 · apache log4j 2.
إرسال تعليق